URGENT SECURITY CHECK · LIVE SOURCE VERIFIED 12 NOV 2026
Did you know hackers may be able to run code on your ticket site - and put customer data at risk?
The live ticket page exposes WordPress 6.8.3. NVD includes that release in the affected range for CVE-2026-119977, a critical RCE during a full-package core-upgrade window. If still unpatched, a successful exploit could put customer records at risk. Verify and patch now.
Potential customer-data exposure
A server takeover could put stored or processed customer information at risk.
Passport/payment-data access is not confirmed; exposure depends on the ticket system’s data and payment architecture. No breach is known from this review.
Vendor fix
WordPress 7.1.4 is the security release.
The flaw enables unauthenticated code execution during a full-package core upgrade window. Confirm the deployed version and patch state immediately.
Live public source checked 12 Nov 2026 04:36 UTC: generator meta tag and asset query strings expose WordPress 6.8.3. This verifies version disclosure and affected-range overlap, not exploitation or customer-data theft.
01 · Security evidence · confirmed vs unknown
Patch status is the first decision. Data exposure is the risk to rule out.
Confirmed advisory
RCE
NVD lists CVE-2026-119977: WordPress Core versions 4.7 through 7.1.3 affected; unauthenticated code execution during the core-upgrade window.
Fix released
7.1.4
WordPress published 7.1.4 on 28 Oct 2026 as a security release and specifically mentions an upgrade-process weakness leading to RCE during upgrade.
Public source confirmed
6.8.3
Live ticket-page generator metadata and WordPress asset URLs expose version 6.8.3, which is in NVD’s affected range. Patch state and whether the upgrade-window condition remains present still require operator confirmation.
Customer impact: remote code execution can provide a route to server compromise. Treat customer records as potentially at risk until the system owner verifies version, patch state, logs and data handling. Do not claim passport/payment records were accessed without evidence.
Next
Action
Evidence to close
1 · Today
Owner confirms core + plugin versions on ticket subdomain; compare with official advisory.
Review upgrade/web logs and payment-data boundaries; escalate to incident response/security specialist.
Authorized findings, remediation and customer-impact assessment
Sources: NVD CVE-2026-119977 (published 31 Oct 2026; Wordfence CNA) · WordPress 7.1.4 security release (28 Oct 2026). Public homepage links to ticket.chiangmainightsafari.com; no ticket CMS access or penetration test.
02 · Search demand · KWFinder · Chiang Mai
Follow the question path from “what can we do?” to ticket.
DiscoverThings to do in Chiang Mai
3,800 / mo
Search demand estimate · KD 14
ChooseChiang Mai Night Safari
17,400 / mo
Search demand estimate · KD 35
EvaluateNight Safari ticket
320 / mo
Search demand estimate · ticket intent
ConvertNight Safari price
80 / mo
Search demand estimate · CPC $0.53
Where the site appears today
“chiang mai night safari”Official page · #3
“things to do in Chiang Mai at night”Not in returned top 5
A dated Mangools SERP snapshot showed the official programme page at position 3 for the branded query. Broader evening-activity results favored travel publishers, directories and discussion pages.
Build the missing bridge
“Is Chiang Mai Night Safari worth visiting?”
“What time do the shows start?”
“How much are tickets and what is included?”
“How do we get there / can we book online?”
These are query-path hypotheses, to validate with fuller keyword, PAA and first-party data before prioritizing content.
Proposal: turn core visitor questions into authoritative Thai and English pages, connect them to current schedules/tickets, and keep facts consistent across the main and ticket domains.
KWFinder MCP · location Chiang Mai, Thailand (ID 21036), Any Language · retrieved 12 Nov 2026 · estimated monthly search volumes: brand seed 17,400, “things to do…” 3,800, ticket 320, price 80. Estimates are not Search Console impressions or site traffic. Mangools SERP snapshots: brand query · night activity query.
03 · Query fan · supplied AI Search Grader evidence
The prompt set is wide. Too many questions miss the visitor’s booking path.
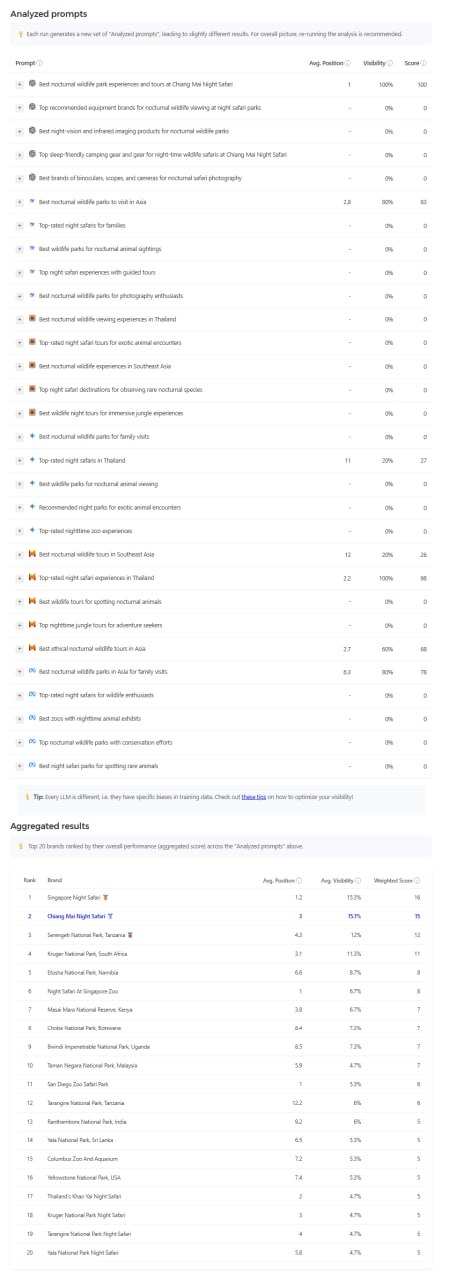
Client-supplied screenshot · query list and aggregate brand table. Snapshot date not visible.
What the screenshot reports
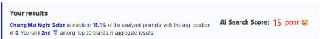
AI Search Score15 · Poor
Brand match in analyzed prompts15.1%
Average position when visible3
Aggregate rank among top 10 brands#2
Platform-specific grader output; not an independent rerun and not a universal AI visibility metric.
Query-fan diagnosis: the prompt list mixes visitor discovery with equipment/product queries. A broad prompt fan can dilute insight if many prompts do not match the visitor’s actual decision.
Rebuild the prompt fan around intent
Discover: family-friendly evening activities in Chiang Mai
Compare: best night safari / wildlife experience near Chiang Mai
Evaluate: show schedule, ticket inclusions, accessibility, transport
Book: current ticket options, price, booking steps, changes
Recommendation: retain the grader’s current prompt set as a baseline, tag prompts by journey stage and relevance, then monitor a cleaner Thai/English set with prompt-level citations and dates.
Image evidence supplied by Alex in this conversation. Numbers above are transcribed from that screenshot only; platform, date range, prompt count and model coverage should be captured from the full export before setting a target.
04 · The visibility gap · AI Search Grader
Present in AI answers sometimes. Not yet reliably chosen.
15 / 100
AI Search Score · “Poor” in supplied snapshot
Brand is listed 2nd among 10 brands, but overall weighted score remains low. Rank among peers and broad visibility are different measures.
What to change
Entity clarity
Describe the experience, official ticket link, location, schedules and services consistently on first-party pages.
Answer depth
Publish concise, up-to-date answers for the high-intent questions in the query fan.
Citation readiness
Use attributable, crawlable pages with clear headings, authorship/ownership, source links and accurate structured data.
Trust signals
Resolve ticket-subdomain security status, then communicate verified trust and booking facts clearly.
No AI score improvement is promised. Recheck using the same tool, prompts, market and model set to compare like with like.
Source: client-supplied Mangools AI Search Grader screenshot; reported 15.1% prompt visibility, average position 3, #2 among top 10 brands, score 15 / Poor. Screenshot date and full settings not visible. AI grader evaluates its configured models/prompts; do not equate with Google AI Overviews or all AI answers.
05 · Proposed 30-day engagement
Secure the booking engine. Then widen the discovery funnel.
Workstream
Days 1–5
Days 6–15
Days 16–30
Proof
Security first
Verify CVE, core/plugins and booking data boundaries
Patch, access review, logs and authorized exposure assessment
Close findings; document incident and backup readiness
Version/advisory evidence; patch + assessment record
SEO / query fan
Expand KWFinder and SerpApi/PAA query research
Map Thai/English discovery → booking intents to pages
Optimize priority pages and interlink to ticket path
Query set, SERP captures, page changes
AIO / GEO / AEO
Reconcile grader prompts; set baseline metadata
Build Q&A content and sourceable entity facts
Rerun same prompt set and log citations
Tool/date/model/prompt-level report
Commercial note
Scope, price and service commitments are not specified here; no pricing or forecast has been invented. Final proposal should be aligned after access, market/language priorities and scope confirmation.
Data needed to finish the baseline
Ticket platform owner + authenticated version confirmation; Search Console/GA4 read access; current grader export with date and settings; approved SerpApi key or authorized API connection.
Immediate decision: ask the ticketing owner to confirm and patch the reported WordPress version before further promotion of the booking journey.
Data sources used: NVD + WordPress.org security release; KWFinder MCP (Chiang Mai); Mangools SERP checker snapshots; user-provided AI Search Grader screenshots. SerpApi direct API was not run: SERPAPI_KEY is not configured in this environment. No Search Console/GA4 data or security scan available.